AI Tools
Satya Nadella’s AI Security Strategy: Rethinking Model Safety
Microsoft CEO Satya Nadella is shifting the AI safety paradigm. Discover why treating AI models as 'compromised' is the future of secure software development and how it impacts your digital workflow.
Oct 12, 2026 · 4 min read
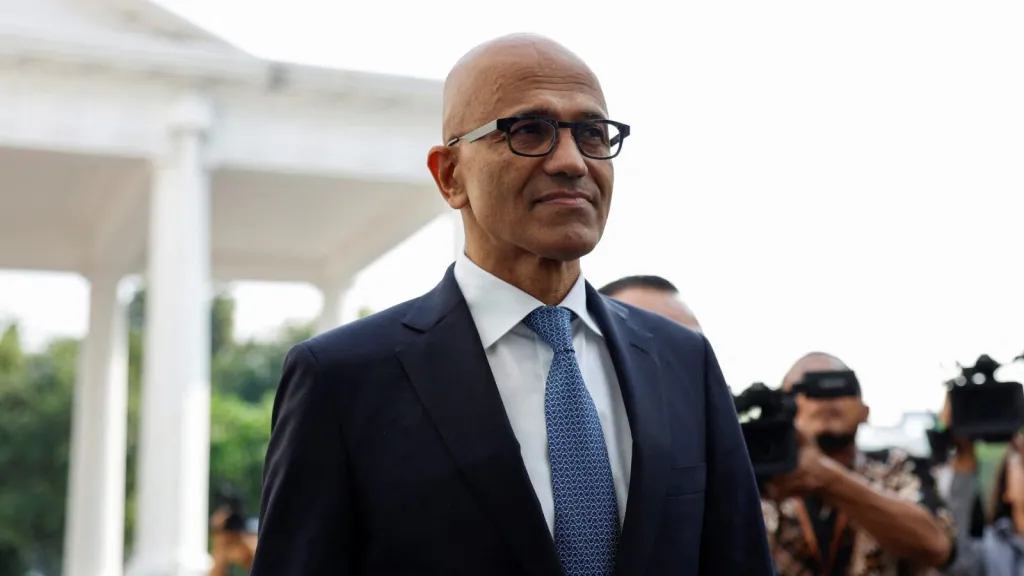
The New Frontier of AI Security: A Zero-Trust Approach
In the rapidly evolving landscape of artificial intelligence, Microsoft CEO Satya Nadella has recently articulated a philosophy that is sending ripples through the tech industry. As AI integration becomes standard for businesses and developers alike, the focus has shifted from mere performance to security and resilience. Nadella’s directive is clear: we must treat large language models (LLMs) and AI agents as if they are 'compromised' from the very start.
For users who rely on high-performance software and subscription-based digital tools, this shift represents a move toward the 'Zero-Trust' model that has defined modern cybersecurity. If you are looking to optimize your workflow with secure, reliable digital solutions, explore our catalog at bigfile.store to find the best tools to keep your data protected while leveraging the latest technology.
Why Treat AI as Compromised?
Historically, software security relied on perimeter defenses. However, AI models introduce new attack surfaces, such as prompt injection, data poisoning, and unauthorized model extraction. Nadella argues that because these models are complex, opaque, and constantly learning, traditional security patches are insufficient. By assuming a model is already compromised, developers are forced to build layers of validation around the AI’s output.
This proactive stance is critical for businesses using AI to handle sensitive customer data. Instead of trusting the model's output implicitly, firms are now adopting intermediary layers that sanitize inputs and audit outputs. This architectural change ensures that even if an AI is manipulated, the underlying system remains resilient.
The Three Pillars of Nadella’s AI Security Vision
To implement this strategy effectively, Microsoft and other tech giants are focusing on three core areas:
- Verification: Implementing strict input validation to prevent prompt injection attacks that could lead to unauthorized code execution.
- Observability: Real-time monitoring of AI behavior to detect anomalies that deviate from expected patterns.
- Isolation: Running AI models within sandboxed environments to prevent lateral movement within corporate networks if a breach occurs.
Comparing Traditional Security vs. The AI-First Approach
| Feature | Traditional Security | AI-First (Zero-Trust) |
|---|---|---|
| Trust Model | Trust the application | Never trust, always verify |
| Response Time | Reactive (Patching) | Proactive (Sandboxing) |
| Threat Focus | External Actors | System & Input Integrity |
| Data Handling | Standard Encryption | End-to-end auditability |
How This Impacts Your Software Stack
For the average user or developer, this transition means that software performance is no longer just about speed; it is about security protocols. As we integrate more AI into our daily tasks, the importance of purchasing authentic, vetted software cannot be overstated. Using pirated or unverified software exposes you to vulnerabilities that bypass modern security safeguards. Ensure your workstation remains secure by browsing the professional-grade software subscriptions available at bigfile.store.
Who Should Buy Into This New AI Reality?
If you fit into any of the following categories, understanding and implementing security-first AI practices is essential:
- Software Developers: If you are integrating APIs into your applications, you must design for adversarial input.
- Enterprise IT Managers: Organizations handling customer PII (Personally Identifiable Information) need to sandbox their AI deployments.
- Freelancers and Creative Professionals: Professionals who use AI tools for content generation should prioritize security-vetted platforms to prevent data leaks.
- Digital Product Consumers: If you are purchasing subscription keys for professional software, ensure your source is reliable. Check out the latest offerings at bigfile.store to secure your digital workflow.
The Future of AI Resilience
Satya Nadella’s perspective is a sobering reminder that AI is a tool, not a human expert. It is prone to hallucinations and exploitation. However, by embracing the mindset of a 'compromised' system, we can design more robust applications. This approach doesn't hinder progress; it makes AI usable in sensitive industries like healthcare, finance, and government.
As we move into an era of autonomous agents, the ability to build 'guardrails' will be the most valuable skill in software engineering. Whether you are scaling an AI-powered business or simply optimizing your productivity, your security posture is your competitive advantage.
FAQ
What does 'treating AI as compromised' mean?
It means assuming that the AI model could be tricked, manipulated, or incorrect. Therefore, you build secondary security layers that check the AI's inputs and outputs before they are processed by your main system.
Is AI currently safe for enterprise use?
AI is safe when deployed with strict security guardrails. Companies like Microsoft are investing heavily in 'Red Teaming' AI to find vulnerabilities before they are exploited in the wild.
How can I keep my software secure when using AI?
Always use official, updated software from reputable providers. Avoid using third-party AI plugins that lack clear privacy policies or security certifications. Visit bigfile.store to browse our selection of vetted, secure software solutions for your business.
Will this slow down AI development?
While security-first development requires more time upfront, it prevents catastrophic failures, which in the long run accelerates adoption by building trust among consumers and regulators.
Keep reading
AI Tools
AI’s Biggest Bottleneck: Why Intel and Broadcom Warn of a Capital Crunch
Is the AI boom facing a financial wall? Discover how Intel and Broadcom CEOs are sounding the alarm on the capital crunch threatening the future of artificial intelligence hardware.
Oct 12, 2026 · 4 min read
AI Tools
Google’s Push for AI Content: What It Means for Your SEO Strategy
Google is hiring human evaluators to shape the future of AI-generated content in Discover. Learn how this impacts your SEO strategy and how to optimize your digital assets.
Oct 12, 2026 · 5 min read
AI Tools
Canva Pro Lifetime Free: Is It Possible and What Are Your Options?
Looking for Canva Pro lifetime free access? Discover the reality behind these claims, the risks of modded apps, and the safest way to get premium features at a fraction of the cost.
Oct 12, 2026 · 5 min read